
AI, Automation and Data Security: A Practical Guide for Event Marketers

Event marketers should be able to adopt new technology confidently, without creating unnecessary exposure for their audiences, organisations or commercial information. That requires proportionate controls, informed decisions and regular housekeeping.
Marketing teams have more technology at their disposal than ever. But every new tool also raises questions about what information we're sharing, who can access it and what happens to that information afterwards.
On 30 October 2026, a new initiative concerning website controls over AI training brought one aspect of that debate into focus: how much control should organisations have over the information they make available to AI systems?
It's a timely question for us at Marketing Alchemist. We've recently been conducting our own security and data housekeeping review, examining the tools we use, the information we retain, our account permissions and how we manage AI within everyday marketing workflows.
As an agency working with event organisers, we regularly handle information entrusted to us by clients. That makes responsible data handling an operational responsibility, not simply an IT consideration. Reviewing our own practices has also prompted us to look more closely at the decisions marketing teams make every day.
Because the challenge isn't whether we should use AI, automation or external marketing platforms. These tools offer genuine commercial benefits. The question is how to use them efficiently, reach the audiences we need to reach and avoid introducing unnecessary risk along the way.
From event photography and audience databases to platform permissions and AI tools, this article examines where those risks arise, what marketing teams can reasonably control and when specialist advice is needed.

The data breaches and cyber attacks of the past few months show how close this has come to everyday marketing work:
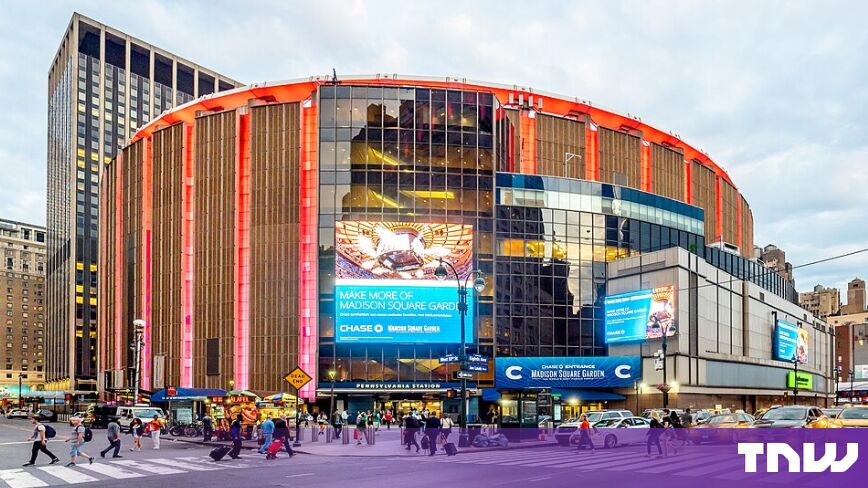
New York, June 2026. Hackers published 45GB of data from the venue group Madison Square Garden after a ransom deadline passed, including facial recognition records captured as visitors entered. They claim 26 million records, a figure not independently verified.
Email marketing, September 2026. Attackers broke into 138 accounts at the email marketing provider Brevo, exported contacts from 43 of them and used 6 to send phishing emails to subscribers from the companies’ own domains.

Singapore, September 2026. The data protection regulator recorded the country’s first AI-related data breach, after a marketing employee used an AI-written script for a bulk email that showed 95,364 members’ email addresses to other recipients. The regulator pointed to missing testing, review and AI usage policies.
UAE, April 2026. The head of cyber security for the UAE government said daily attacks on the country had risen from around 200,000 to around 600,000, and named event services among the industries targeted.

A venue’s visitor records, an email marketing platform and a bulk send written with AI: each of these stories sits squarely in marketing’s territory, and each could happen to an event organiser in any market.
Who in your organisation is responsible for AI risk and event marketing data security?
In most organisations, privacy, legal, security and IT own AI risk, and marketing uses the tools. The IAPP’s AI Governance Profession Report (2025) found privacy (57%), legal (55%), security (53%) and IT (52%) are the functions most often given responsibility for AI governance.
That split creates a blind spot. The people accountable for the risk sit a floor or a timezone away from the people uploading speaker headshots, exporting registrant lists and connecting new tools to the CRM. They can only govern what they know about, and in most event businesses nobody has told them how marketing works day to day.
In AI governance, organisations using AI systems developed by other providers are often described as deployers. Their responsibilities depend on the applicable laws, the tools they use and how those tools process information.
For marketing teams, four familiar data protection principles provide a useful starting point:
Principle | What it means for you |
Purpose | Use attendee data and photos only for what people agreed to when they registered |
Minimisation | Give each tool the least data it needs to do its job |
Retention | Delete data and uploads once the job is done |
Transparency | Say in your privacy policy how you use data, AI tools included |
Steps to follow
List every tool your team uses that touches attendee, speaker or exhibitor data.
Note which of those tools use AI, including features added to tools you already had.
Send the list to whoever owns privacy or IT, with a request for 30 minutes to walk them through it.
Can you upload event photos to AI Tools to make social graphics?
Potentially, but first check what your organisation has permission to do with the images.
Most event registration terms include photography provisions covering promotional use.
However, permission to photograph someone and publish their image does not necessarily establish an appropriate basis for uploading that image to a third party AI platform.
Before using event photography in AI tools, check your registration terms, privacy notice, the tool's data handling arrangements and any applicable restrictions on sharing personal information with external providers.

The difference matters. When you upload a photo to ChatGPT or an image generator, you’re sending it to a third party that may store it and, on some plans, use it to improve its models. A clause that says “we may use your photograph in our marketing” may not stretch to that. Under the EU and UK GDPR and most modern data protection laws, a photo of an identifiable person is personal data, and some markets go further.
In the UAE, the legal position may involve personal data protection requirements alongside laws governing privacy and the unauthorised capture, disclosure or alteration of images. The applicable requirements depend on the circumstances, so ask your legal or data protection team to review your intended use before uploading identifiable photographs.
So before the next edition opens registration, read your photography clause and privacy policy side by side with how your team actually uses photos today.
Top tips for using event photos in AI tools
Use photographs that your organisation has the appropriate rights and permissions to process. Check that the intended AI use is covered, regardless of whether the image was taken by an official photographer or a member of your team.
Favour crowds, stands, products and hands. Wide shots and detail shots make strong graphics and carry far less risk than identifiable close-ups.
Ask before you alter a face. Get written permission before you edit, cut out or generate a likeness of a named speaker.
Check your plan’s training setting, and use a business plan where your inputs stay out of training.
Delete the upload once the graphic’s done. The finished asset lives in your design folder, and the tool doesn’t need to keep the original.
Which of your tools hold attendee data, and do they need all of it?
Every tool connected to your registration system potentially has access to personal data. Some also retain copies, creating additional places where that information needs to be protected. The question to ask of each tool is simple: if it were hacked tomorrow, how much would it give away?
Event marketing stacks grow one edition at a time. An amplifier such as INGO or Gleanin gets connected to turn registrants into promoters, a project board gets set up for the launch, an export goes to the agency for a retargeting audience, and three editions later every one of those copies is still sitting there. Data you no longer need is still data you’re responsible for, and the Brevo breach above shows what happens when an attacker reaches a marketing platform’s contact lists.
MarTech Hygiene
Amplifiers and referral tools. Do they hold only the fields they need to create share links and personalised graphics, usually a name, company and email? Are past editions’ registrants still stored, or have they been exported, archived and deleted from the tool?
Project management (Monday.com, Asana and similar). If you run several editions on one workspace, does the board you’re working on need every past edition’s contacts, contracts and supplier details attached? Archive closed editions into a restricted space, and keep personal data out of task comments and attachments where you can.
Shared drives and inboxes. How many spreadsheets of registrants, badge scans and lead lists are sitting in shared folders and email threads? Each one is a full copy, usually with the widest access in the business.
Agencies and freelancers. Which exports have you sent them, and have they confirmed deletion when the job ended?
Steps to follow
Make a one-page data map: tool, what personal data it holds, which editions, who has access.
For each tool, cut the fields it holds down to the minimum it needs to work.
Export and archive past editions to one secure, access-controlled location, then delete them from the live tools.
Ask agencies and freelancers to confirm deletion of anything you’ve sent them in writing.
Review the map at the end of every edition, before the next campaign starts.
How do you keep your AI tools clean?
Treat AI workspaces as another place where business information can accumulate. Conversations, uploaded files, connected applications and saved personalisation settings may retain information beyond the task for which it was originally shared.
Different platforms have different controls for memory, retention, training and deletion. Removing a conversation does not necessarily remove associated files, saved memories or information held through connected services.
For confidential work, use tools and account configurations approved by your organisation. Check the provider's retention settings, restrict unnecessary data sharing and review what remains stored after a project finishes.
Safe to share | Keep it out |
Published event information, agendas and press releases | Registrant, delegate and visitor lists |
Anonymised or rounded figures | Names, emails and phone numbers |
Copy drafts and campaign ideas | Passport, visa or ID details |
Your own brand guidelines | Exhibitor contracts and unpublished rates |
Photos covered by your consent wording | Unannounced speakers and anything under NDA |
Top tips for AI tool hygiene
Use approved business tools with appropriate privacy and retention controls. Avoid entering identifiable personal data unless it is necessary and authorised.
Review saved memories, conversations and uploaded files regularly, deleting information according to your organisation's retention policy.
Delete uploaded files from projects and workspaces once the work’s done.
Disconnect connectors you no longer use, such as Google Drive, email or your CRM.
Remove leavers, agencies and freelancers from shared AI workspaces.
Check the training setting on every plan the team uses.
How do you make the clean-up happen automatically?
Where your business plan offers a retention policy, set one, so old chats and files delete themselves. Where it doesn’t, make the clean-up a recurring monthly task, either in the team calendar or as a scheduled task in the AI tool itself, with one named owner who logs that it’s done. A 30-minute job on the first Monday of the month stops 12 months of data piling up.
How do you get AI tools to recommend your show while protecting your data?
Open your public marketing pages to search engines and AI answer bots, so ChatGPT, Perplexity and Google can find, recommend and cite your show. Then keep people, images and paid-for content away from the crawlers that collect training data, and put anything private behind a log-in.
The balance works because these are now different bots doing different jobs. Answer bots fetch a page when someone asks a question and link back to you, which is the visibility every show wants. Training crawlers collect content in bulk to teach future AI models, usually with no link and no credit. A buyer asking which energy exhibitions to attend in 2027 is served by the first kind, so your dates, audience and reasons to exhibit should be wide open to it.
Regulators are clear that “public” doesn’t mean “free to take”. In August 2023, 12 data protection authorities, including the UK’s ICO, published a joint statement saying personal information on public websites is still protected by privacy law, and that organisations hosting it should guard against unlawful scraping. A follow-up statement from 17 authorities added that the same applies when personal data is used to build AI models. For an event organiser, the speaker page, the exhibitor directory and the photo gallery are all hosted personal data.
What changed that impacted event marketing data security this week?
On 30 October 2026, Google, Microsoft, Anthropic and OpenAI announced support for a single line in a website’s robots.txt file that asks every AI company to skip that site when training its models, and submitted a draft standard to the Internet Engineering Task Force. Microsoft also announced a separate AI Grounding setting covering pages fetched to answer someone’s question. Microsoft and OpenAI expect to support the standard in the coming months, and Google next year.
For event organisers, emerging crawler controls may provide more options for distinguishing between content made available for search and content that website owners do not want used for AI training. Implementation and support will vary by provider, so ask your developer to confirm which controls are currently available before changing your website configuration.
Which bots should you welcome, and which should you limit?
Your developer can give each bot its own rules in robots.txt, and can set them by section: open the exhibit and visit pages, for example, and close the gallery folder.
Bot | Run by | Its job | On a show website |
Googlebot | Search results, including AI Overviews | Welcome everywhere public | |
OAI-SearchBot | OpenAI | Answers and citations in ChatGPT search | Welcome on marketing pages |
Claude-SearchBot | Anthropic | Answers and citations in Claude | Welcome on marketing pages |
PerplexityBot | Perplexity | Answers and citations in Perplexity | Welcome on marketing pages |
GPTBot | OpenAI | Collects content to train models | Your call on marketing pages; limit on people and galleries |
ClaudeBot | Anthropic | Collects content to train models | As GPTBot |
Google-Extended | Decides whether your content trains Google’s AI models; blocking it leaves you in Google Search | As GPTBot | |
CCBot | Common Crawl | Builds an open dataset many AI developers train on | Consider limiting |
There’s a case for letting training crawlers read your top-level marketing pages too: models trained on them will already know your show’s name, sector and city, even before they search. The protection matters on the pages about people and the content you’ve paid to create, such as speaker photos, galleries, exhibitor contacts and gated reports. Bot names and their jobs change, so ask your developer to check each company’s current documentation before setting the rules.
Top tips for your website’s images
Publish fewer identifiable close-ups in public galleries, at lower resolution.
Ask search engines to leave gallery images out of image results using noimageindex and X-Robots-Tag (see the glossary).
Add the AI training opt-out once your website platform supports it.
Move full galleries and exhibitor contact details behind an attendee log-in.
Find old edition pages and PDFs that still list past attendees or exhibitors, and take them down.
“No right-click” and download-blocking scripts stop casual saving only, since anyone can take a screenshot, so treat them as a deterrent and rely on the layers above.
Which pages should AI be able to see?
Page | Search and AI answer tools | AI training | What to do |
Home, dates, why exhibit or visit, FAQs, press releases | Let them in | Your call | Write key facts as text, never only in images |
Blog and reports | Let them in, for citations | Consider opting out | Add the training opt-out when supported |
Speaker pages | Approved bios only | Consider opting out | Keep personal contact details off |
Exhibitor directory | Company names and categories | Opt out | Contact names and emails behind a log-in |
Photo galleries | Limit | Opt out | Consented images only, fewer close-ups |
Registration, delegate lists, networking app, rate cards | Keep out | Keep out | Log-in, with noindex as a backstop |
Questions to send your developer
What does our robots.txt allow and block today, and does our hosting or CDN block anything it doesn’t mention?
Can we add noimageindex to the gallery pages and an X-Robots-Tag to the image folder?
Which pages and PDFs from past editions are still live, especially attendee or exhibitor lists?
Can gallery images be published at lower resolution, with full-size files on request?
When the new AI training opt-out is supported, can we add it while still letting AI search tools cite our public pages?
Can the gallery and exhibitor contact details move behind a log-in?
What should be on your monthly marketing security checklist?
Set aside 30 minutes each month to review your marketing team's security housekeeping. Some actions will take longer or require support from IT, legal or external partners, but a regular review helps identify what needs attention before the next event cycle.
Assign one person to coordinate the review, record outstanding actions and follow up with the relevant owners.
Review saved memories, conversations and uploaded files in approved AI tools. Remove information that is no longer required, in accordance with your organisation's retention policy.
Delete files uploaded to AI projects and workspaces
Disconnect any AI connectors you no longer use
Remove leavers, agencies and freelancers from every channel and tool
Check two-step verification is on for social accounts, email platform, website and registration system
Change any password that’s been shared since last month
Check amplifier and project tools hold only the current edition’s data
Confirm agencies have deleted any exports from last month
Check the website gallery for new close-ups of identifiable people
Log that the clean-up’s done, and anything you found
Where should you start this week?
Start with the systems and information your marketing team uses every day. Share your photography practices with your data protection team, ask your developer to review the website controls and schedule your first monthly access and data review.
Before using a platform, ask:
Purpose: What are we trying to achieve, and is this tool necessary?
Data: What information does it need, and can we share less?
Access: Who can see, download or change that information?
Retention: What happens to the information when the work is finished?
Accountability: Who owns the decision, and who needs to approve it?
Marketing teams understand how information moves through an event campaign. IT, legal and data protection specialists understand the controls needed to protect it. Bringing those perspectives together is the first step towards reducing unnecessary exposure.
At Marketing Alchemist, we help exhibition and conference organisers review their marketing operations, technology and data workflows, identifying opportunities to improve processes and reduce operational risk.
If your marketing systems have grown across multiple events, platforms and teams, we'd be happy to help you assess how everything fits together.
Frequently asked questions
Can I upload event photos to AI Tools to generate graphics? Potentially. Check that you have an appropriate legal basis, the necessary image rights and permission to process the photographs through an external AI provider. Your privacy notice and the tool's data handling arrangements should also be reviewed.
Does my event privacy policy need to mention AI? If your team uploads attendee data or photos into AI tools, your privacy policy should say so. Send your data team a short note on how marketing uses photos and AI today, and ask them to confirm the wording.
What does noindex mean? Noindex is an instruction on a web page asking search engines to leave that page out of their results. Search engines have to be able to read the page to see the instruction.
How do I stop AI crawlers using my website images? Ask your developer to add noimageindex and X-Robots-Tag to your gallery, add the new AI training opt-out when your platform supports it, and move full galleries behind a log-in.
How often should event marketers change passwords and review access? Review access at the start of every edition and the day after the show closes, and change any password that has been shared. Two-step verification on every account cuts the risk further.
Should I block AI bots from my event website? Block selectively. Let search engines and AI answer bots read your public marketing pages so AI tools can recommend your show, and limit training crawlers on pages about people, photo galleries and paid-for content.
Appendix: the terms
Term | What it means |
Crawler (or bot) | A computer program that visits websites automatically and reads them. Search engines use crawlers to build their results, and AI companies use them to collect material for their tools. |
robots.txt | A short public file on your website that tells crawlers which pages they may visit. Think of it as a sign on the door: polite visitors follow it, but it doesn’t lock anything. |
noindex | A note on a single web page asking search engines to leave it out of their results. The crawler has to be allowed to read the page to see the note. |
noimageindex | A note asking Google to leave the images on a page out of its image search results. |
X-Robots-Tag | The same kind of note, attached to files such as images and PDFs, which can’t carry a note of their own. |
AI training | When an AI company uses text and images from the internet to teach its models. Once something has been learned this way, it’s very hard to take back. |
AI training opt-out | A new single line for robots.txt, announced on 30 October 2026, asking AI companies to leave your website out of their training. Support is rolling out over the coming months. |
AI deployer | An organisation that uses an AI tool someone else built. A marketing team using ChatGPT or an image generator is a deployer. |
Memory (in AI tools) | Notes an AI assistant keeps about you between conversations. Deleting a chat may leave its memory behind. |
Temporary chat | A conversation an AI tool doesn’t save to your history or memory. |
Retention policy | A setting that deletes old data automatically after a fixed time. |
Two-step verification | A second check when you log in, such as a code sent to your phone, so a stolen password alone isn’t enough. |
Password manager | An app that creates and stores strong passwords, so your team can log in without knowing or sharing them. |
Data map | A simple list of every tool that holds personal data, what it holds and who can see it. |
Phishing | A fake email or message designed to trick someone into clicking a link or handing over details. AI now makes these look very convincing. |
Scraping | Copying information from websites automatically and in bulk. |
CDN | A service that delivers your website quickly around the world. It can also block crawlers, sometimes without anyone noticing. |

